
Trust & Security
Read-only, scoped and revocable. Here is exactly what we see.
Montro connects read-only to the systems you already run. This page sets out exactly what we collect, where it's kept and what controls apply.
Trust
Three pillars of security
How we protect your data

Residency
Customer data stays in Europe
Hosted on AWS in Frankfurt. Sub-processors listed below.

Architecture
Built on enterprise primitives
TLS 1.3, AES-256, RBAC, MFA, audit logging throughout

Certifications
Security programme
Pen-tested by a third party. ISO 27001 certification in progress.
DATA RESIDENCY
European data. Staying in Europe.
All data processed and stored by Montro remains within the European Union. This is not a configuration option or a paid add-on. It is the architecture.
Our infrastructure runs on AWS eu-central-1 Frankfurt, operating under German and EU law.There is no Schrems II ambiguity to navigate.

AWS - Frankfurt, Germany
Compute, database, and storage infrastructure. Governed by German and EU law.

European by default
Your data is never replicated outside the EU without your explicit, documented consent.

DPA specifies residency
Data residency terms are included in all Data Processing Agreements - not buried in privacy policies.

EU-located or approved
All sub-processors are in the EU or operate under a valid transfer mechanism.
Data Access
Exactly what we access - and exactly what we don't.
Montro reads from four read-only sources, plus an optional browser extension that is off by default. Here is what each one reads, and what Montro never touches.
Sign-in and OAuth grants
Microsoft Entra ID, Google Workspace or Okta: which apps people sign in to, and which have been granted access.
Directory and licences
Users, groups and assigned licences, so each supplier is tied to the people and teams who use it.
Finance and ERP
Supplier names and spend from your finance systems, so suppliers nobody signs in to still appear.
Cloud accounts
Read-only access to AWS, Azure or Google Cloud for the services running in your accounts.
Browser extension (optional, off by default)
Chrome or Edge, installed only if you choose. Metadata only.
What Montro never accesses
Message content, file contents, passwords, or the data held inside the apps on your register.
Security Architecture
How we secure what you share with us
Security is built into Montro's infrastructure, not applied on top of it. Below are the specific controls governing your data at rest and in motion.
01
TLS 1.3
Encryption in transit
All data moving between your environment and Montro's infrastructure is encrypted via TLS 1.3. Older protocol versions are rejected.
02
AES-256
Encryption at rest
All customer data stored in Montro's infrastructure is encrypted at rest using AES-256. Key management follows AWS KMS best practices with strict access controls.
03
Strict data segregation
Tenant Isolation
All customer data is scoped to organisation identifiers enforced at the application and database layers. Cross-tenant access is architecturally prevented.
04
Role-based (RBAC)
Access Controls
Granular permissions govern which users in your organisation see which data. Administrative access is separately scoped and tied to identity - not shared credentials.
05
Read-only by default
Least Privilege
All OAuth scopes requested during integration are the minimum required for discovery. We request read-only access wherever technically possible.
06
Every access event logged
Audit logging
All access events, configuration changes, and administrative actions are logged with timestamps. Logs available to account administrators on request.
07
MFA enforced
Authentication
Multi-factor authentication is enforced for all Montro team members with production access. SSO-based access available for customer admin accounts.
08
VPC isolation
Network security
Production infrastructure runs inside an AWS Virtual Private Cloud with strict ingress and egress controls. No unnecessary public surface area.
GDPR & PRIVACY
Your data. Your rights. Our obligations.
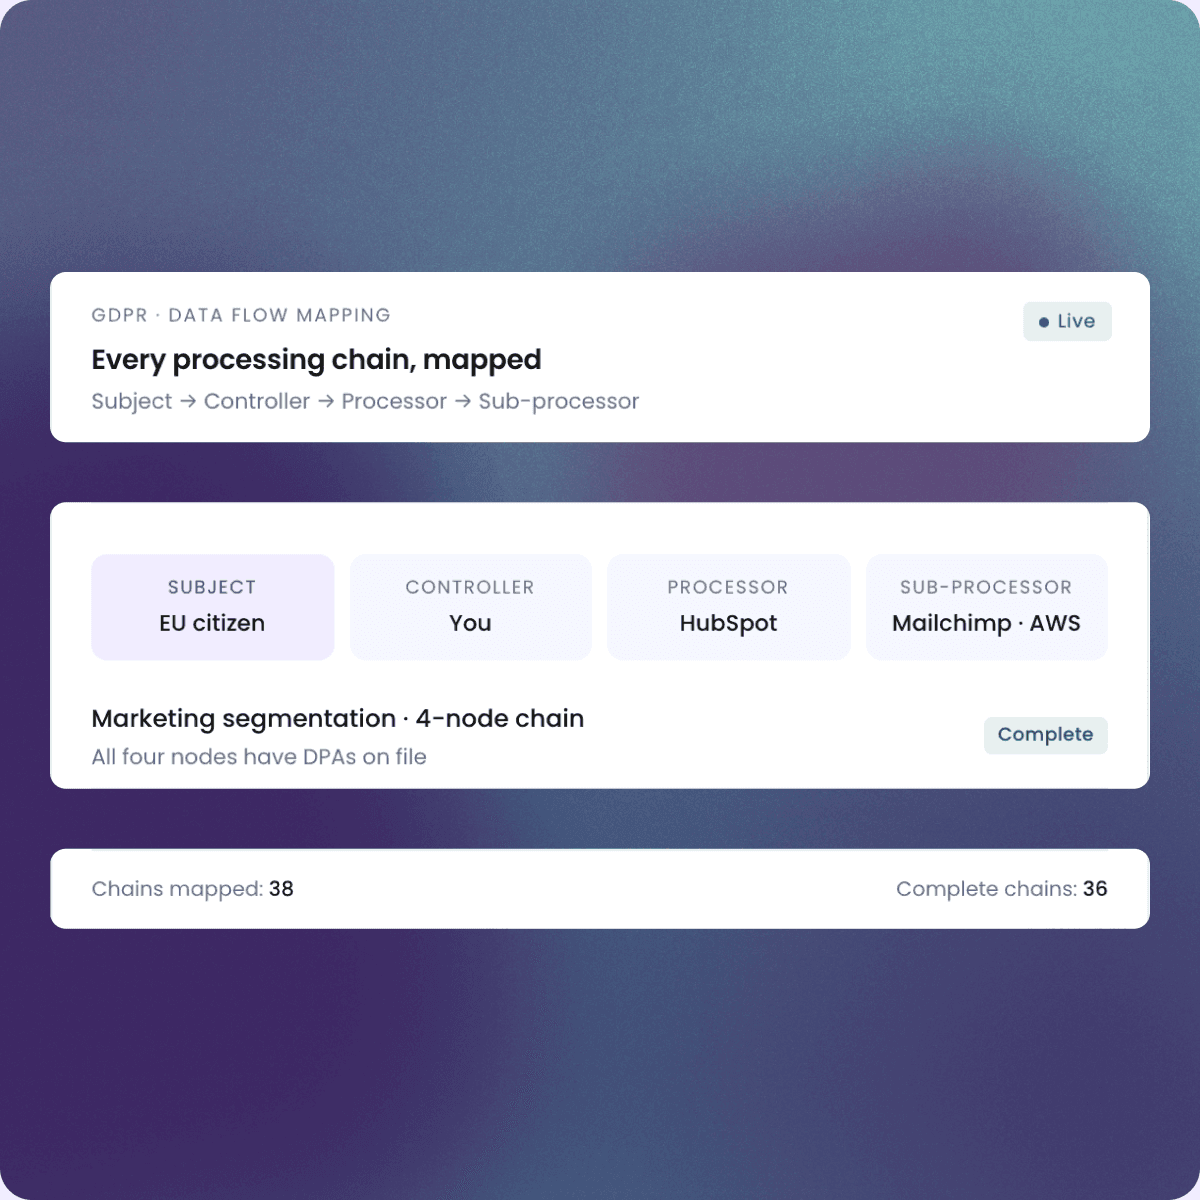
Under GDPR, Montro acts as a data processor on your behalf. You remain the data controller. Your GDPR obligations don't change because you use Montro - they become easier to fulfil.

Your organisation
You determine the purposes and means of processing personal data. GDPR obligations - lawful basis, data subject rights, breach notification - sit with you.

Montro
We process personal data only on your documented instructions, only for delivering the Montro service, and only for as long as your agreement runs.
Our Own Governance
We keep our own records
We run Montro on ourselves. Our own suppliers and AI services sit in our own register, each with an owner and a recorded decision. The AI tools we use, including the models in our product, are classified against the EU AI Act, and we keep our own Article 30 record of processing.
Certifications and Roadmap
What we have - and what we're building toward

GDPR-aligned: DPA, sub-processor list and Article 28 terms on request
Documented DPA, sub-processor register, retention schedules, breach response procedure, and data subject rights handling - included in all agreements.

AWS Standard Security Controls
Encryption at rest and in transit, VPC network isolation, IAM access controls, CloudTrail audit logging, and automated backup - all active in production.

Internal Security Policy Documentation
Access control policy, incident response procedure, acceptable use policy, and change management controls. Available on request for vendor security questionnaires.

Third-Party Penetration Test
Penetration-tested by a third party. Summary available under NDA.

ISO 27001 Certification
ISO 27001 certification in progress

Annual Third-Party Penetration Testing
Once our initial pen test is complete, annual testing by an accredited firm will become part of our standard security programme.
Sub Processor
Who we share your data with
We use a limited number of third-party sub-processors. All are within the EU or operate under a valid GDPR transfer mechanism. We notify customers with 30 days advance notice of any material changes.
| Sub-Processor | Purpose | Data Location | Legal Mechanism |
|---|---|---|---|
| Amazon Web Services (AWS) | Primary infrastructure - compute, database (RDS), storage, networking | EU (Frankfurt) | Standard Contractual Clauses + AWS DPA |
| HubSpot | CRM and communication metadata - used for customer onboarding and support contacts only | Legal Mechanism | Standard Contractual Clauses + HubSpot DPA |
| Stripe | Billing and payment processing - handles payment data; does not process operational customer data | EU | Standard Contractual Clauses + Stripe DPA |
Amazon Web Services (AWS)
- Purpose
- Primary infrastructure - compute, database (RDS), storage, networking
- Data Location
- EU (Frankfurt)
- Legal Mechanism
- Standard Contractual Clauses + AWS DPA
HubSpot
- Purpose
- CRM and communication metadata - used for customer onboarding and support contacts only
- Data Location
- Legal Mechanism
- Legal Mechanism
- Standard Contractual Clauses + HubSpot DPA
Stripe
- Purpose
- Billing and payment processing - handles payment data; does not process operational customer data
- Data Location
- EU
- Legal Mechanism
- Standard Contractual Clauses + Stripe DPA
Found a Vulnerability? Tell Us
If you discover a security vulnerability in Montro, please report it responsibly before public disclosure. We take all reports seriously and commit to responding quickly.
Our commitments to security researchers
- We acknowledge receipt of your report within 24 hours
- We investigate and respond with a timeline within 5 business days
- We keep you informed of remediation progress throughout
- We will not take legal action against good-faith security researchers who follow this process
Note : Please do not access or modify customer data, interrupt services, or perform social engineering as part of your research. Allow us reasonable time to remediate before any public disclosure.
Send vulnerability reports
to [email protected]. Please include a description of the vulnerability, steps to reproduce, and potential impact. PGP encryption is available on request.
Contact
Talk to us directly
Have a security questionnaire to complete? Need documentation for your DPO? Want to discuss our architecture before starting a pilot? We respond directly - not through a ticketing system.
Security
Vendor security questionnaires, pen test documentation, architecture questions, vulnerability reports
Privacy & GDPR
DPA requests, sub-processor lists, data subject rights queries, GDPR documentation