
Thirty days to compliance
In 30 days, you will have a board-ready report covering every SaaS app and AI tool in your organisation - mapped to GDPR, DORA, NIS2, and the EU AI Act. At no cost.
Deliverable
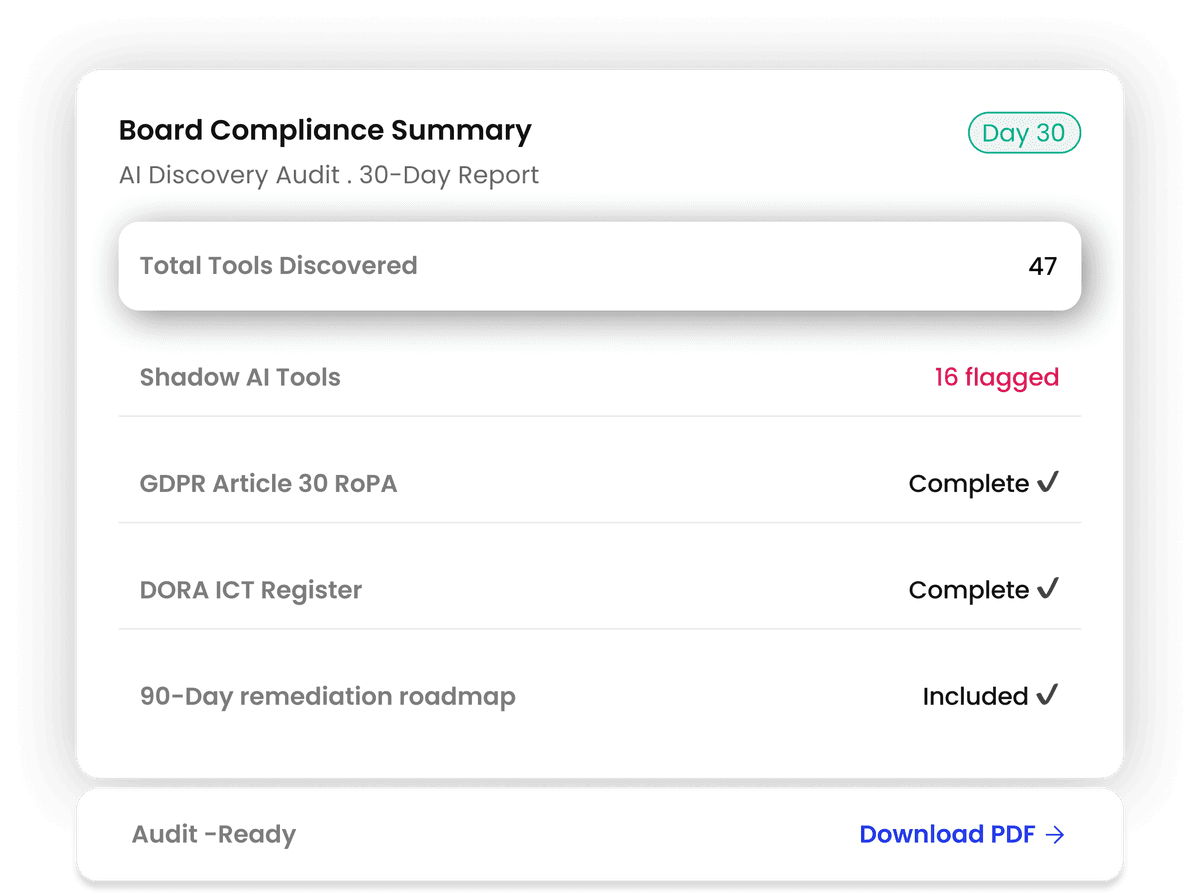
Inside your 30-day audit report
A complete SaaS and AI tool inventory mapped to every regulation that matters. Shadow AI included. Risk-rated. Ready for your board.

SaaS inventory
Every application and AI tool in use, by department and user count. Nothing hidden.

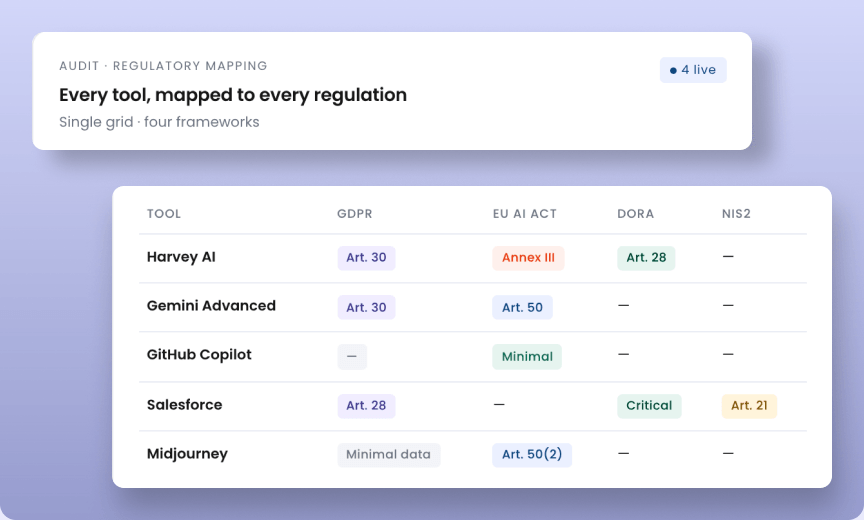
Regulatory mapping
GDPR, DORA, NIS2, and EU AI Act classifications with specific risk ratings and compliance gaps flagged for each tool.
Deliverable
Register templates
Draft DORA ICT Register, Article 30 Records of Processing Activity gap analysis, and NIS2 supply chain exposure summary ready for your team.
Three steps
How the audit works
Connect your identity provider, then we do the rest
Step one
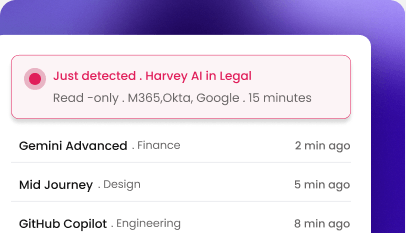
Automated discovery
We connect via SSO or Microsoft 365. No agents. No code. Fifteen minutes.
Step two
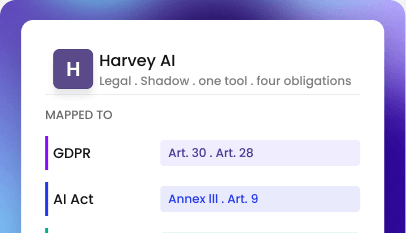
Regulatory mapping
Every tool classified against GDPR, DORA, NIS2, and the EU AI Act automatically.
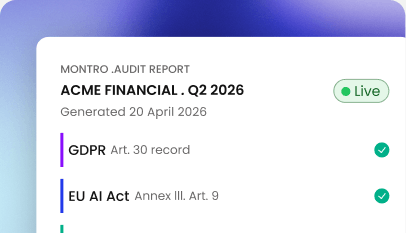
Step three
Audit-ready reporting
Board-ready PDF with risk ratings, remediation steps, and a 90-day roadmap.
Process
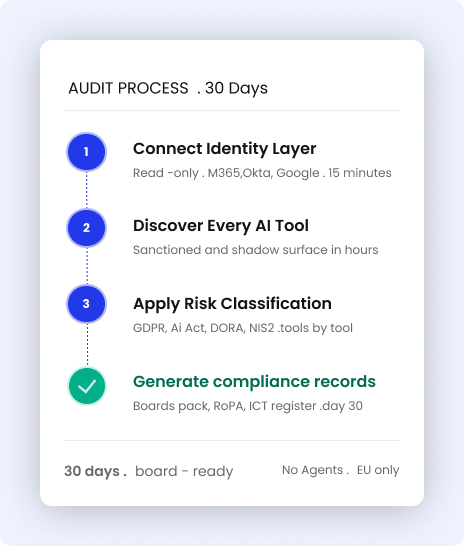
Four steps to complete visibility
Your organisation's AI inventory emerges in hours, not months. Each tool is classified against EU AI Act criteria and documented automatically, ready for regulators.

Connect your identity layer
SSO, Microsoft 365, or cloud infrastructure integrates in minutes without disruption.

Discover every AI tool
Shadow AI and approved systems surface automatically across departments and teams.

Apply risk classification
Unacceptable, high, limited, or minimal—each tool tagged instantly without manual effort.

Generate compliance records
Article 9 assessments and audit reports ready the same day for boards.
Connect your identity layer
SSO, Microsoft 365, or cloud infrastructure integrates in minutes without disruption.
Discover every AI tool
Shadow AI and approved systems surface automatically across departments and teams.
Apply risk classification
Unacceptable, high, limited, or minimal—each tool tagged instantly without manual effort.
Generate compliance records
Article 9 assessments and audit reports ready the same day for boards.
Assurance
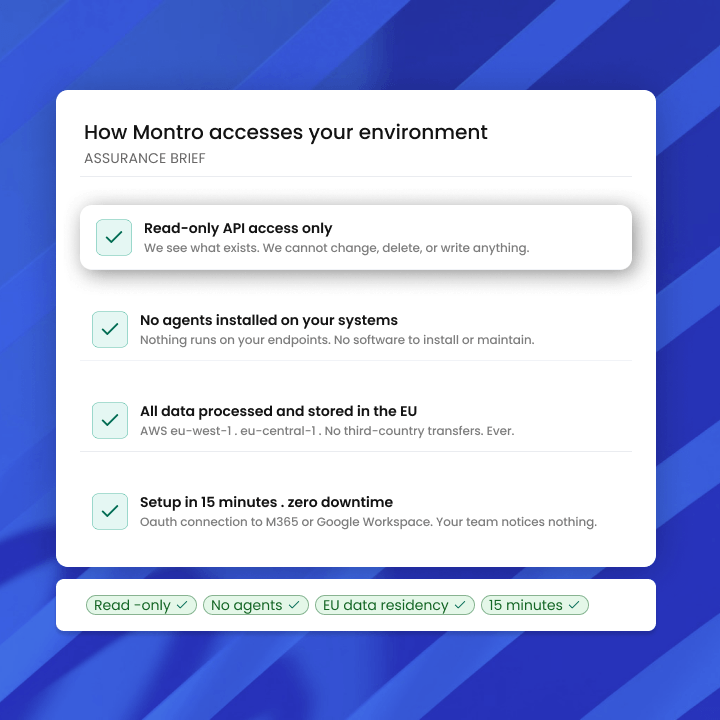
No disruption to your environment
Read-only access. No agents. No infrastructure changes. You review everything before we begin.
- Read-only API access
- No agents installed in your system
- All data processed and stored in the EU (The same changes will go in the image beside this section)


Results
What we find for organisations like yours
Real discovery numbers from European mid-market firms
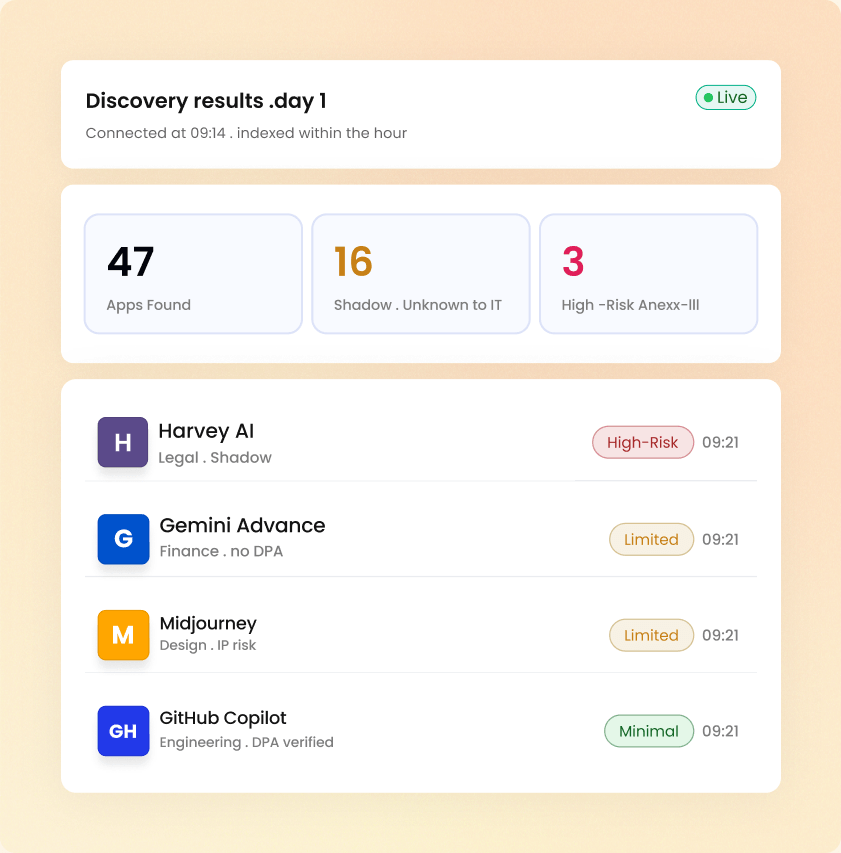
Average AI tools discovered
47
Per organisation, including shadow AI not in IT records
Unsanctioned tools found
34%
Tools in use but not on the official IT-approved list
DORA register gaps identified
23
Average compliance gaps per organisation requiring remediation
Begin
Get in touch
Three fields. Five business days. One complete report.
FAQs
Common questions about the audit process and what comes next
See what happens after the audit
Continuous registers, monitoring, and board-ready evidence — move from a one-time snapshot into ongoing compliance with Montro.