Your employees are not reckless. They are resourceful. When an AI tool helps a marketing manager draft a campaign brief in twenty minutes or lets a developer debug code without a six-week procurement queue, they use it - and they keep using it, whether IT approves it or not. That is not a discipline problem. It is a shadow AI governance gap.
The instinct to respond with blanket bans is understandable but counterproductive. Restriction without education does not eliminate shadow AI, it makes it harder to detect, harder to govern, and harder to address when something goes wrong. The organisations that are reducing exposure are not the ones that block the most AI tools. They are the ones that build the most informed employees.
This guide sets out what an effective shadow AI employee training programme looks like: one that creates informed, compliant behaviour without generating the resentment that pushes usage further into the shadows.
Why Punitive Approaches Backfire
Prohibition without understanding creates concealment, not compliance. The data on this is unambiguous.
THE CONCEALMENT PARADOX
Why banning AI drives it underground - not away
59% of employees admit using unapproved AI tools at work | 39% operate in a policy vacuum - no company AI policy exists or they don't know if one does | 67% of organisations report fewer incidents after implementing security awareness training |
When employees feel that the rules exist to protect IT budgets rather than to protect them or the organisation, they route around those rules. A Cybernews survey of over 1,000 employees found that 59% already admit to using unapproved AI tools - a figure that is almost certainly an undercount, since the survey captures only those willing to disclose it.
The policy visibility gap makes this worse. The same Cybernews research found that 23% of employers have no formal AI policy at all, and a further 16% of employees don't know whether one exists. That combined 39% operating in a policy vacuum cannot be expected to make compliant choices - they have no framework to comply with.
Meanwhile, 85% of employees who have access to approved AI tools still admitted to using unapproved ones in the past year (Cybernews). The problem is not availability. It is policy clarity and trust, and it is what makes shadow AI governance a training problem as much as a technical one.
The goal is not zero AI usage outside approved tools. The goal is informed employees who can make compliant choices - and who trust the process enough to ask before they act. |
The Four Things Employees Need to Know
An effective shadow AI training programme does not attempt to turn every employee into a compliance officer. It gives people the minimum viable knowledge to make responsible choices. That means four specific things:
THE FOUR PILLARS OF EMPLOYEE AI KNOWLEDGE
What every employee must understand before using any AI tool at work
01 WHY IT MATTERS GDPR, EU AI Act & NIS2 obligations explained in plain language - not legalese. | 02 HOW TO REQUEST A clear, frictionless process to request approval for any new AI tool. |
03 PERSONAL ACCOUNTS What employees can and cannot do with personal AI accounts during work hours. | 04 HOW TO REPORT A safe, non-punitive channel to flag a potential AI governance concern. |
1. Why AI Tool Governance Matters - In Plain Terms
Employees switch off the moment training starts with regulatory definitions. Lead with consequences they recognise. When an employee pastes a client contract into a free AI chatbot, three things may have already happened: personal data has left the organisation without a Data Processing Agreement, a record of processing has been missed from the GDPR Article 30 register, and an unclassified AI system has processed data without a risk assessment under the EU AI Act.
The training goal here is not legal literacy - it is intuition. Employees should leave this module with a clear mental model: if the data is sensitive, the tool needs to be approved, and that intuition is the foundation of any effective shadow AI governance culture.
2. How to Request an AI Tool for Approval
The single biggest driver of shadow AI is friction in the approval process. If requesting an approved tool feels bureaucratic or slow, employees will find their own solution. Training on the request process must communicate three things: where to submit the request, how long it takes, and what happens next. Ideally, approval takes no longer than five business days for standard-risk tools, and employees are notified of the outcome either way.
Make the request process feel like IT saying yes, not IT saying wait.
3. What They Can and Cannot Do With Personal AI Accounts at Work
This is the most common grey area and the most common source of unintentional violations. Employees understand that using personal email for company communications is wrong. They do not automatically apply the same logic to shadow AI tools. Training must be explicit: using a personal ChatGPT or Claude account to process company data - even for a routine task - creates the same governance gap as sending company files to a personal Dropbox. The account is outside the organisation's Data Processing Agreement, outside its audit trail, and outside its ability to respond to a data subject request.
Equally important: tell employees what they can do. Using personal AI accounts for genuinely personal tasks, public information, or non-sensitive brainstorming is a different risk category. Give employees the distinction, not just the prohibition.
4. How to Report a Potential AI Governance Issue
Incident reporting is where training culture becomes visible. If employees are afraid to disclose that they have been using an unsanctioned tool, the organisation loses its most important early-warning signal. Training must establish a non-punitive reporting channel - a named team, a form, or a ticketing route - and communicate clearly that reporting a concern is the right behaviour, not evidence of wrongdoing.
EU AI Act Article 73 already requires organisations to report serious incidents involving AI systems. Building internal reporting fluency before regulators require it is not optional - it is preparation. |
Training Format That Works
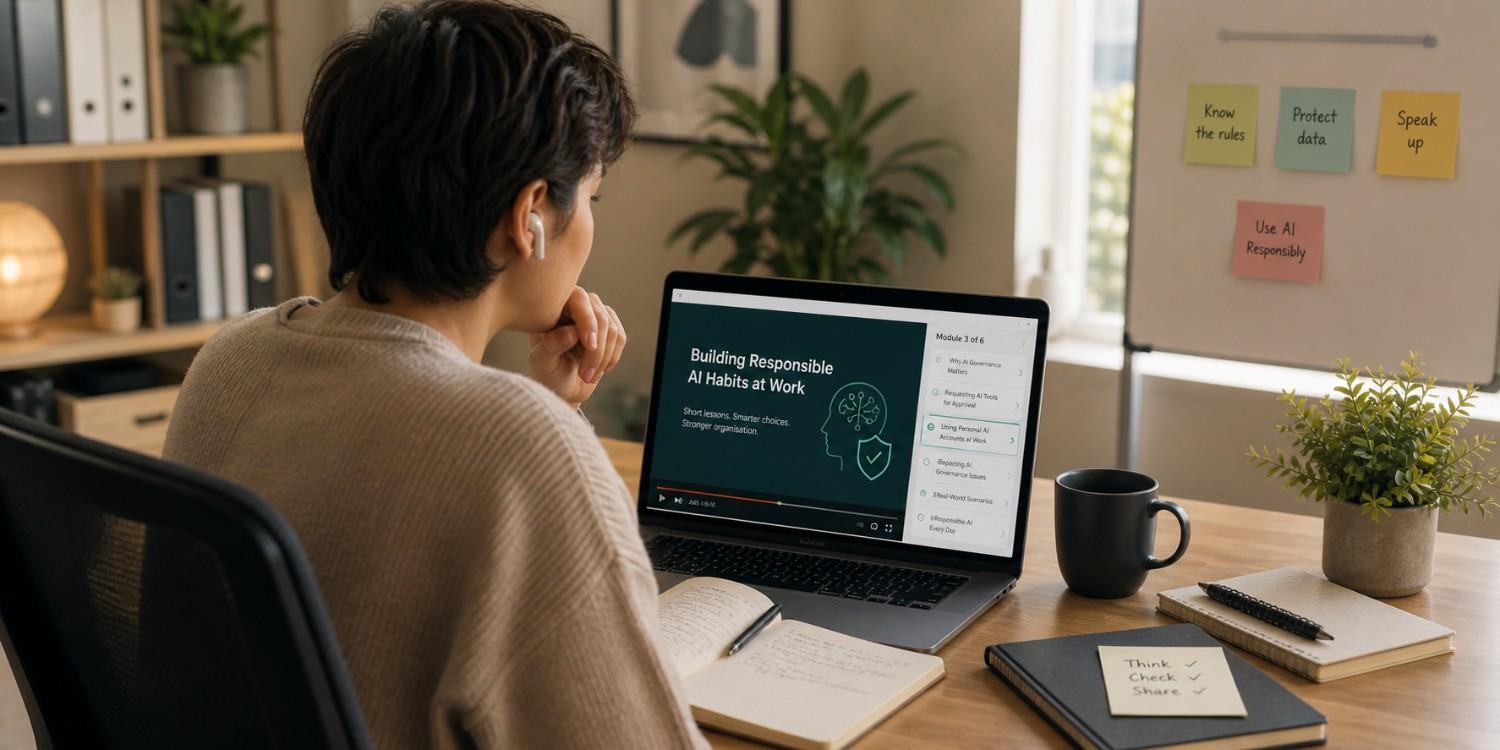
The format of training matters as much as the content. A 90-minute annual compliance lecture on AI regulation will produce low retention, high resentment, and zero behaviour change. Research consistently shows that micro-learning - short, focused sessions of five to ten minutes - outperforms traditional formats across every engagement metric.
TRAINING FORMATS THAT ACTUALLY WORK
Micro-learning drives 50% higher engagement than traditional formats (Gartner / Software Advice)
5-10 MICRO-MODULES Bite-sized sessions - one concept per module, monthly cadence | ▶ REAL SCENARIOS Employees see themselves in the story, not generic examples | ★ MANAGER BRIEF Managers pre-briefed before every rollout - they model the culture | ↺ ANNUAL REFRESH Refreshers timed to regulatory updates, not calendar years |
The practical architecture for a shadow AI employee training programme looks like this - six modules, delivered across the first two quarters, each five to ten minutes long:
MODULE | TOPIC | SCENARIO USED IN TRAINING |
1 | What counts as an AI tool at work | Employee discovers Grammarly has an AI rewrite feature already enabled in their browser - is it in scope? |
2 | Why personal accounts create a GDPR gap | HR manager pastes candidate CVs into a free ChatGPT account to draft feedback - three GDPR failures in one action. |
3 | How to use the approved tool register | Developer wants an AI code review tool - walkthrough of the request-to-approval flow and what a 48-hour turnaround looks like. |
4 | What not to paste into a chatbot | Finance analyst shares a budget spreadsheet with an AI summariser - what data classification applies and why it matters. |
5 | How to report a governance concern safely | Employee realises a colleague has used an unapproved meeting transcription tool for three months - what to do, and what happens next. |
6 | Annual regulatory refresh | What changed in the EU AI Act, GDPR enforcement, or NIS2 guidance this year - and what it means for how employees use AI day-to-day. |
- Real scenarios, not legal lectures. Each module opens with a two-minute scene employees recognise from their own working day. Then walk through which regulation was triggered, what the right path looked like, and what the outcome of each choice would have been. Interactive formats retain information 2.3 times better than passive slide decks - so replace presentations with decision-point walkthroughs wherever possible.
- Manager briefings - one week before every module goes live. Run a 20-minute team lead session in the week before each module is released to employees. The briefing has three components: (1) a one-page talking points sheet summarising what the module covers and the two or three questions employees are most likely to raise; (2) clear instruction on what managers should do if an employee discloses they have already been using a non-approved tool; and (3) a prompt for managers to share one example from their own team's AI use at their next team meeting. Managers who visibly check the approved register before recommending a tool - and who use the request channel themselves - drive adoption more effectively than any module alone.
Manager briefings are where the shadow AI training quietly fails. Not because the managers are unsupportive – because they have been handed a policy summary and asked to answer a list of questions they were never prepared for. An employee asks why a tool they have been using for months is suddenly a problem, and the manager does not know how to answer it. That moment does more damage than any gap in the training programme itself. The briefing has to cover the why, not just the what. - Namita Razdan, Co-Founder, Montro |
- Annual refreshers timed to regulatory events, not calendar years. Module 6 in the curriculum above is not a fixed date - it is triggered by a regulatory event. When the EU AI Act publishes updated implementing guidance, when a significant GDPR enforcement decision lands, or when a high-profile shadow AI incident makes industry news, release a short update module within two weeks. A five-minute "What just changed and what it means for you" module timed to a real event lands far better than a generic annual refresher scheduled in January because the calendar said so.
NIS2 and DORA both mandate ongoing training rather than one-time annual events - making this continuous, scenario-driven curriculum a compliance requirement as well as a pedagogical best practice.
The Approved AI Tool Programme: The Positive Version of Governance
Training tells employees what not to do. An approved AI tool programme gives them something to do instead - and that is far more effective at reducing shadow AI than any restriction.
THE APPROVED AI TOOL PROGRAMME - HOW IT WORKS
Compliance through positive access, not restriction
1 CURATED LIST Maintain a live register of approved AI tools, reviewed quarterly | 2 APPROVED USE CASES Each tool comes with defined scenarios - what it can and cannot do with company data | 3 REQUEST CHANNEL Clear, fast approval workflow for new tools employees discover |
The mechanics are straightforward but the culture signal they send is significant. Maintaining a curated, live register of approved AI tools - with defined use cases for each - removes the friction that drives employees toward personal accounts. Instead of asking "Is this allowed?" and not knowing the answer, employees can check the register and get an immediate, authoritative response.
Each tool on the register should carry four pieces of information: what it can be used for, what data it cannot be used with, which regulatory frameworks it has been assessed against, including the AI risk assessment conducted at the time of approval, and when the assessment was last reviewed. This is not bureaucracy - it is the practical output of an AI governance platform doing its job.
85% of employees who have access to approved AI tools continue to use them - but 69% of those without approved tools said they hadn't used outside AI at all. The approved programme is not a ceiling on AI use. It is a floor. |
The approved programme also changes the conversation employees have with IT. Instead of a relationship defined by restriction, it becomes one defined by enablement, and continuous AI tool discovery running in the background ensures the gap between what is approved and what is actually in use remains visible rather than growing silently.
Measuring Training Effectiveness
A training programme without measurement is a compliance exercise. A training programme with the right metrics is a culture programme. Three indicators tell you whether the shift is happening:
MEASURING CULTURE SHIFT - YOUR GOVERNANCE DASHBOARD
Track these three indicators to know if your programme is working
✓ Self-Assessment Completions Target: >90% completion within 2 weeks of each module rollout | ↑ Approved Request Volume Rising requests = trust in the process. Culture is shifting from hiding to asking. | ! Incident Reports Filed More self-reported incidents = psychological safety. Silence is not safety. |
- Self-assessment completions. Track completion rates within two weeks of each module rollout. Below 90% is a signal that either the training is too long, too infrequent, or not reinforced by managers. Completion is a lagging indicator - but the pattern across modules tells you whether engagement is building or eroding.
- Approved tool request volume. Rising request volume is a positive signal. It means employees are encountering new AI tools, recognising that they need approval, and trusting the process enough to ask. A flat or declining request volume - in an environment where AI adoption is accelerating - is a red flag.
- Incident reports filed. This is the metric most organisations misread. A rising number of self-reported AI governance concerns is not evidence that training is failing - it is evidence that psychological safety is increasing. Employees are naming problems instead of hiding them. That is exactly what a mature training culture looks like.
Over a twelve-month well-run programme, expect meaningful improvement across all three indicators. Companies with AI training programmes report 40% fewer security incidents - not because they reduced AI use, but because employees began making better decisions about which AI they used and how.
READY TO BUILD YOUR SHADOW AI TRAINING PROGRAMME?
Download the Shadow AI Policy Template - the companion resource to this training guide. It includes the approved tool register structure, prohibited practices clauses mapped to EU AI Act Article 5, employee obligation language, and a review cycle framework ready to deploy today.
Download the Shadow AI Policy Template
Frequently Asked Questions
How do you build a shadow AI training programme without creating resentment among employees?
Lead with the reason, not the rule. Employees follow policies they understand the purpose of and ignore ones that feel arbitrary. A training programme that opens with "here is what happens to client data when it leaves our environment without a processing agreement" lands differently than one that opens with "here is our AI acceptable use policy." The goal is intuition, not compliance theatre, employees who understand the risk make better decisions without needing to remember every rule.
How often should shadow AI training be updated and delivered?
Timed to events rather than calendar dates. A fixed annual refresher is less effective than a short module released within two weeks of a relevant regulatory development; an EU AI Act enforcement decision, a significant data breach involving an AI tool, or a new GDPR guidance publication. NIS2 and DORA both emphasise ongoing training and awareness rather than purely point-in-time exercises, which makes the continuous, event-triggered model a regulatory expectation as well as a more effective approach.
What is the right way to handle an employee who discloses they have been using an unsanctioned AI tool?
Treat it as useful information, not a disciplinary matter. The disclosure means the reporting channel is working and the employee trusts the process enough to use it. The response should be a conversation about what the tool was used for, what data it processed, and whether any governance action is needed, not a formal warning. Organisations that punish disclosure stop receiving it. The early warning signal disappears. The exposure continues.
What should an approved AI tool register actually contain?
Four things per tool - what it can be used for, what data categories it cannot process, which regulatory frameworks it has been assessed against, and when that assessment was last reviewed. Without the last item, the register becomes stale without anyone noticing. A tool that was clean at assessment may have had AI features added since, which is why continuous AI tool discovery is the operational complement to the register, surfacing changes the review cycle alone would miss.