Montro

Episode

Why Compliance Isn't Security

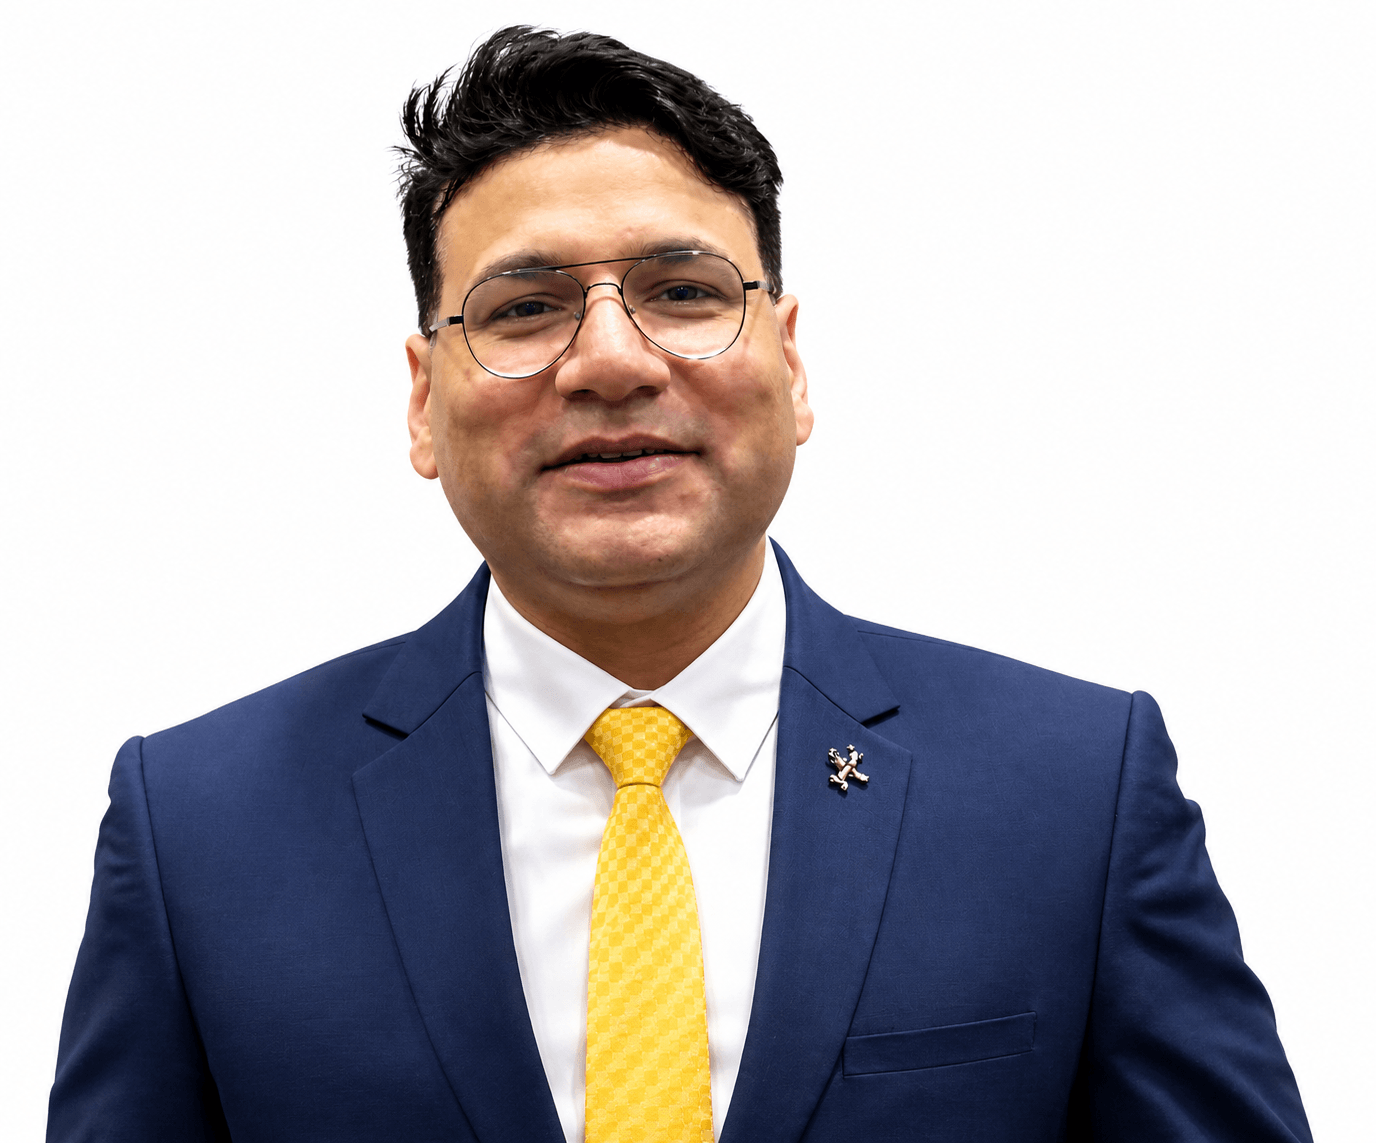
"Compliant" and "secure" are not the same thing. In this episode of Montro In Practice, Ankur Arora sits down with Roopesh Srivastava, a cyber and resilience leader with two decades across military and enterprise, on why tick-box compliance leaves you exposed: people as the weakest link, building security into multi-cloud without slowing the business, getting third-party risk under control, and what NIS2 really asks of you.

Published

31 August 2026

Duration

41 minutes

Guest

About the speaker

Roopesh Srivastava is a cybersecurity and resilience leader with two decades across military and enterprise. A former Director of Cybersecurity and Resilience at the Ministry of Defence, he is now Senior Information Security Architect at eir, where he designs security into complex, multi-cloud environments - including critical national infrastructure.


He describes himself as more practical than bookish, and it shows. This is a conversation about what actually keeps an organisation safe, once the certificates are on the wall.

Episode guest

In this episode

There's a question every board eventually asks its security team: are we secure? And there's a comfortable answer that gets offered back - we're ISO certified, we passed the audit, the box is ticked. Roopesh Srivastava has spent twenty years learning that those two things aren't the same, and this conversation is about the space between them.


Compliant isn't the same as secure


Ask Roopesh what belief he'd push back on hardest, and he doesn't hesitate: that being compliant means being secure. He's sat across from plenty of companies proud of their certifications - ISO, SOC 2, the lot - and his response is blunt. A certificate tells you a company has taken an approach. It doesn't tell you the company is safe.


"Having a firewall with no rules is no worth. You could be compliant by having a firewall, but what makes you secure is a different thing entirely." - Roopesh Srivastava


Compliance isn't useless. It's just a floor, not a finish line. A firewall with no rules still shows up on the checklist. A policy nobody follows still counts as a policy. Real security is a lot of moving parts working together properly, and no audit can promise you that.


So where does the real work sit? Not in the tooling, Roopesh says. Tools come and go - you buy something today, it's out of date tomorrow, you swap it out. Chasing the next tool is a short game.


What holds is people and process. For most of the last decade, he points out, the weakest link in almost any system hasn't been the software - it's been a person. Someone who lost a credential, clicked the wrong link, got talked into something they shouldn't have. And that leads him somewhere a lot of security teams still resist: security can't live with one department in the corner. Everyone in the building is part of it, whether they realise it or not.


That changes what a security leader is even there to do. Less gatekeeper, more enabler. Set security up as a separate function that sits in judgement over everyone else, and you become the person the business quietly works around. Build it into how the business already runs, and it stops being a blocker.


And with third parties, start by looking


One thread runs underneath all of it: you can't secure what you can't see. Roopesh is direct about where third-party risk begins - not with a clever control, but with an inventory. The breaches he's watched land in recent years tended to come through a vendor someone had approved and then forgotten. Until you actually know who you've let in, the rest is guesswork.


The risk was never the certificate on the wall. It's everything the certificate doesn't capture, the rules behind the firewall, the person behind the keyboard, the vendor nobody wrote down.

More

More from the series

Worth your time – security, privacy, and resilience leaders across Europe.

When Controls Meet RealityOperational Resilience, DORA, Risk Management, Financial Service
FriSept 2026

When Controls Meet Reality

A framework that reads well for auditors can still fail when pressure hits. In this episode of Montro In Practice, Ankur Arora sits down with Emmanuel Ranchin, VP of Information Protection Governance at State Street, on the gap between documented controls and lived ones: why compliant isn't the same as resilient, how big institutions break where silos meet, and what DORA really asks of the board.

Watch now
Compliant on Paper Isn't Compliant in RealityGDPR, EU AI Act, Privacy Engineering, AI Governance, Data Protec
TueSept 2026

Compliant on Paper Isn't Compliant in Reality

A policy can say all the right things and still not describe what's actually running. In this episode of Montro In Practice, Ankur Arora sits down with Abhishek Bansiwal - DPO, lawyer, and privacy-and-AI governance leader, on the gap between paper compliance and lived reality: why "anonymised" often isn't, why the AI Act is closer to a product safety law than a privacy one, and the one question every leader should start asking - "so what?"

Watch now
Why People Break the Rules Around AI at WorkShadow AI, Behavioural Science, AI Adoption, Human Behaviour
MonAug 2026

Why People Break the Rules Around AI at Work

Rules on paper rarely survive contact with people. In episode two of Montro In Practice, Ankur Arora sits down with behavioural scientist David DeFranza on why employees reach for AI tools they're not meant to use: the gap between personal productivity and organisational risk, why we behave more rationally when we think we're dealing with AI, and where that quietly becomes dangerous.

Watch now
View all

Don't miss the next conversation

Get new Expert Series episodes and governance insights in your inbox.

Browse episodes